"Share this Info and Help a Friend"
NEW: AI Mobile and Desk Phone Service!
"AI Reception, AI Summary, Call Recording Transcription"
Answer Calls and Text on your Desk Phone / Computer / Mobile Phone / Tablet.
TIME = LIFE "TeQ I.Q. Increases your TIME"
TeQ I.Q. is for Customers who Embrace Change, Want Real Support With More Solutions to Increase Sales and Have More Time!
Call Robert at 619-255-4180 to Easily set you up!
TeQ I.Q. Computer Repair, TeQ I.Q. TV, TeQ I.Q. Mobile, TeQ I.Q. Internet, TeQ I.Q. Phone
8.8 Million Records Weak Passwords:
YouTube Video "8.8 Million Records Weak Passwords"
What if something as simple as a "123456" password was the only thing that stood between cybercriminals and your customers' personal information? That's allegedly what happened in Denmark, where an attacker accessed 8.8 million identity records with alarming ease. Learn more here.
What Led to the Danish National Registry Breach?
In September 2026, an unauthorized individual accessed Denmark's Central Register of Persons (CPR), a national database containing personal information about residents. The registry holds names, addresses, birth dates, and unique identification numbers used across government and financial services.
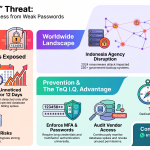
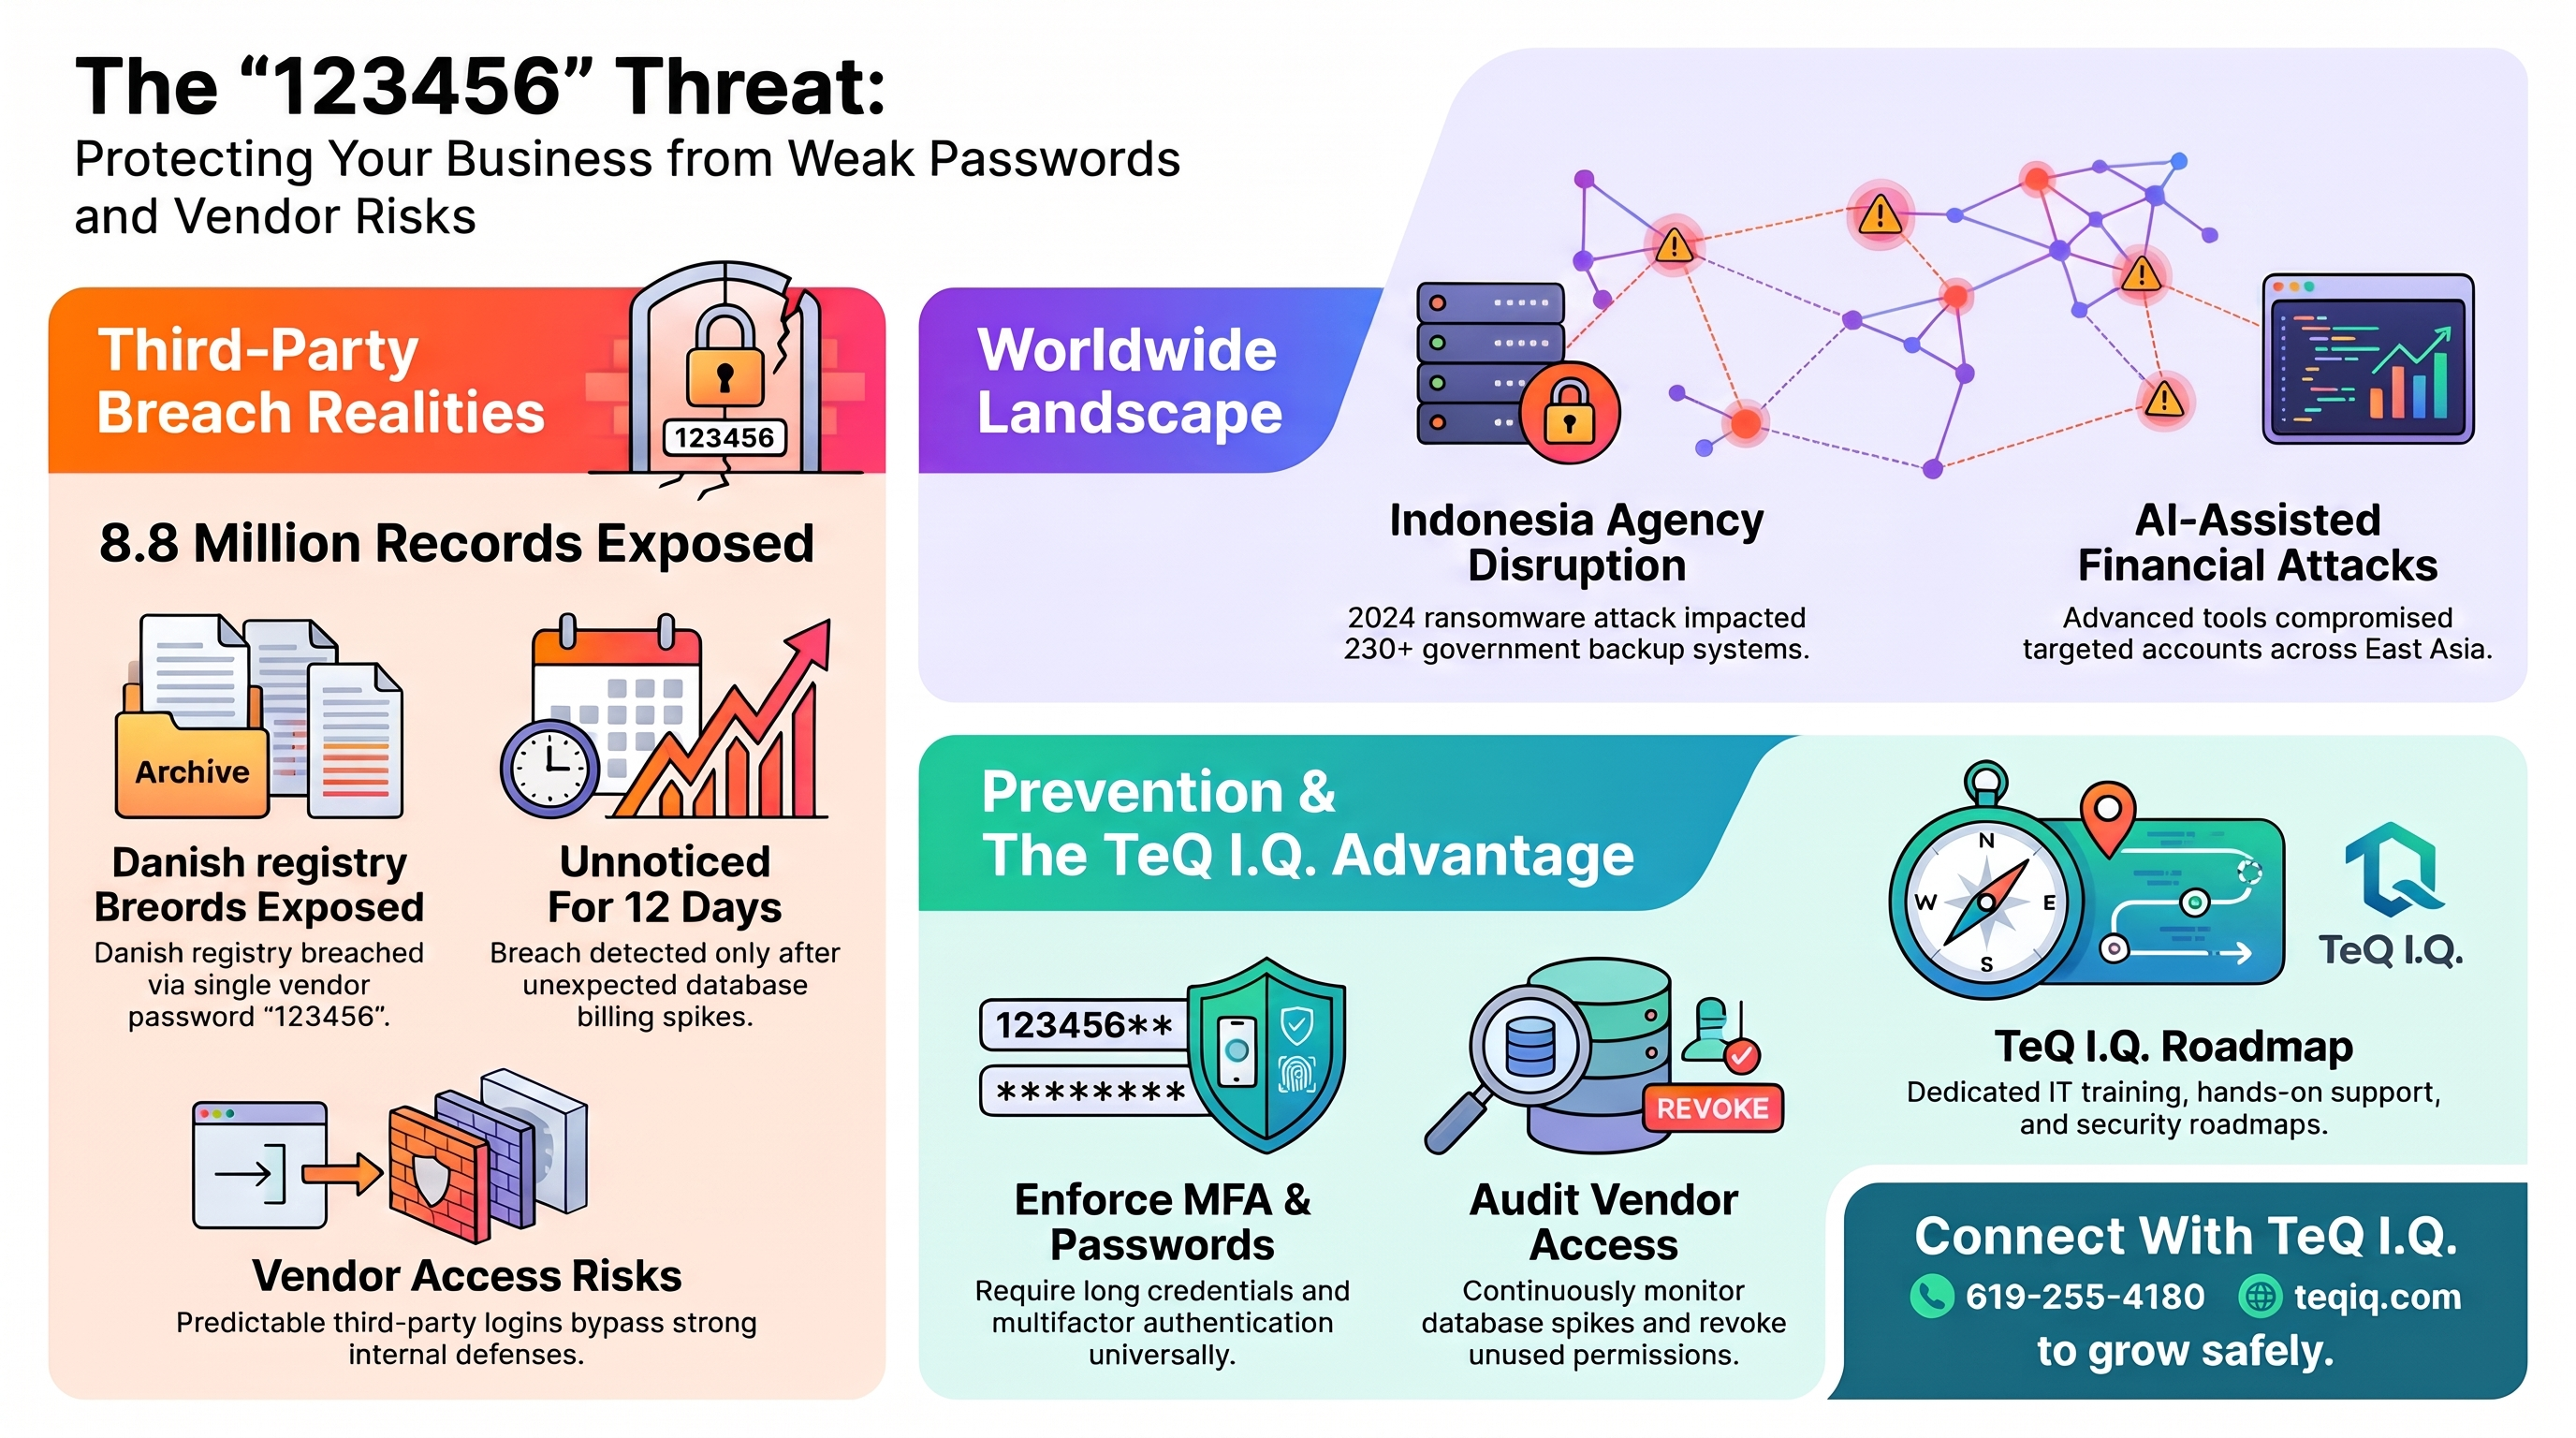
Instead of directly breaching CPR infrastructure, the alleged culprit exploited access belonging to Pays ApS, a Danish IT and data services company authorized to retrieve registry information. The attacker claimed three separate company accounts shared the notoriously weak "123456" password, which let them retrieve roughly 8.8 million records without authorization. This went unnoticed for 12 days until an unusually large invoice revealed suspicious database activity.
Is Your Business Safe From Similar Attacks?
The person claiming responsibility expressed disbelief at the company's poor security practices. They also insisted they had no intention of leaking or selling the stolen information, arguing that organizations handling sensitive records have a responsibility to protect them properly.
However, this doesn't necessarily eliminate the risks of sensitive personal data exposure. Once someone retrieves confidential information without authorization, there's no guarantee it will remain private.
The bigger concern for businesses is third-party access because even well-protected internal systems can become vulnerable when an outside service provider relies on predictable login credentials. Think about the vendors that handle your customer records, payment systems, or employee information. How closely do you monitor their security practices?
No Organization Is Immune to Cybersecurity Threats
This isn't an isolated issue; major institutions worldwide have experienced breaches and disruptions that exposed vulnerabilities in their digital infrastructure. Recent incidents include:
- Indonesia (2024): A ransomware attack disrupted over 230 public agencies and revealed serious shortcomings in the government's data backup systems.
- Taiwan (2026): Hackers allegedly used AI-powered tools to infiltrate government systems, gaining access to at least 85 accounts and stealing over 2,500 personnel records.
- South Korea (2026): Suspected AI-assisted attacks compromised several financial institutions, including Shinhan Bank and KB Kookmin Bank.
Although the circumstances varied, these cases share a troubling pattern: established organizations aren't immune to security failures, and all it takes sometimes is one overlooked vulnerability.
Don't Let Weak Password Security Compromise Your Operations
Your company doesn't need a government-sized database to attract threat actors. Take the proactive route and strengthen your password authentication systems and other data protection measures:
- Require long, unique passwords for every business account.
- Enable multifactor authentication, especially for systems containing sensitive information.
- Use a password manager to discourage predictable or reused credentials.
- Review third-party access and revoke unnecessary permissions.
- Monitor unusual login activity and unexpected spikes in database requests.
- Regularly audit employee accounts for weak or outdated credentials.
Advanced cybersecurity tools have their place, but they won't compensate for subpar security practices. No customer database should depend on something as easily guessed as a "123456" password.
Unless you have a highly capable in-house IT team, we recommend working with a provider that offers training, support, and an implementation roadmap like TeQ I.Q. has.
Ask How TeQ I.Q. can help You or Your Business. Call 619-255-4180 or Go To Web Site https://www.teqiq.com/
TeQ I.Q. is for Customers who Embrace Change, Want Real Support With More Solutions to Increase Sales and Have More Time!
If this tip helps and you would like to donate click on the button. Thanks In Advance.
________________________________________________________________________________________________________
"Fortune Favors, Who Value Time over Money!"
"TeQ I.Q. was the 1st IT Company to Deliver Cloud Solutions since 2003"
Tech issues taking up your Time?
"TeQ I.Q. Makes Your Technology Secure and Protected"
Do you have Tech Frustrations like your Computer, Internet, Phone, Cellphone, Camera, TV, Car?
"We Take Away Your Tech Frustrations and Give You the Free Time You Deserve!"
Call Robert to ask all your Technology questions.
For Free Consultation Call Now Robert Black at (619) 255-4180 or visit our website https://www.teqiq.com/
Chase Bank and Others Trust TeQ I.Q. with their IT and TeQnology so can you!