"Share this Info and Help a Friend"
NEW: AI Mobile and Desk Phone Service!
"AI Reception, AI Summary, Call Recording Transcription"
Answer Calls and Text on your Desk Phone / Computer / Mobile Phone / Tablet.
TIME = LIFE "TeQ I.Q. Increases your TIME"
TeQ I.Q. is for Customers who Embrace Change, Want Real Support With More Solutions to Increase Sales and Have More Time!
Call Robert at 619-255-4180 to Easily set you up!
TeQ I.Q. Computer Repair, TeQ I.Q. TV, TeQ I.Q. Mobile, TeQ I.Q. Internet, TeQ I.Q. Phone
Microsoft Targeted in Phishing:
YouTube Video "Microsoft Targeted in Phishing"
Are your establishment's Microsoft cloud accounts as secure as they seem? A recent phishing operation shows how threat actors can exploit authentication workflows to access sensitive business data.
Why More Businesses Are Moving to the Cloud
Cloud technology now sits at the center of many everyday business operations. Companies use platforms such as Microsoft 365 to keep essential tools and information within one connected digital environment.
When adopted correctly, cloud-based tools can bring the following worthwhile benefits:
- Flexible access to essential workplace resources
- Centralized storage for important business files
- Easier collaboration between employees and departments
- Scalable resources that adapt to changing needs
Unfortunately, the growing value and popularity of these platforms also make them appealing to cybercriminals. Microsoft Security Research has tracked a sophisticated campaign since May 2026 that targets employees through familiar authentication procedures.
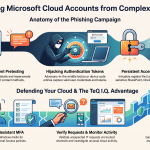
How Does the Campaign Unfold?
This passkey-themed phishing campaign goes beyond sending a convincing email and hoping someone clicks. Threat actors combine direct contact with carefully crafted authentication prompts to make their requests appear legitimate.
These social engineering attacks can ultimately result in identity and cloud compromise. The scheme develops through several stages, with each one bringing the intruder closer to valuable company resources.
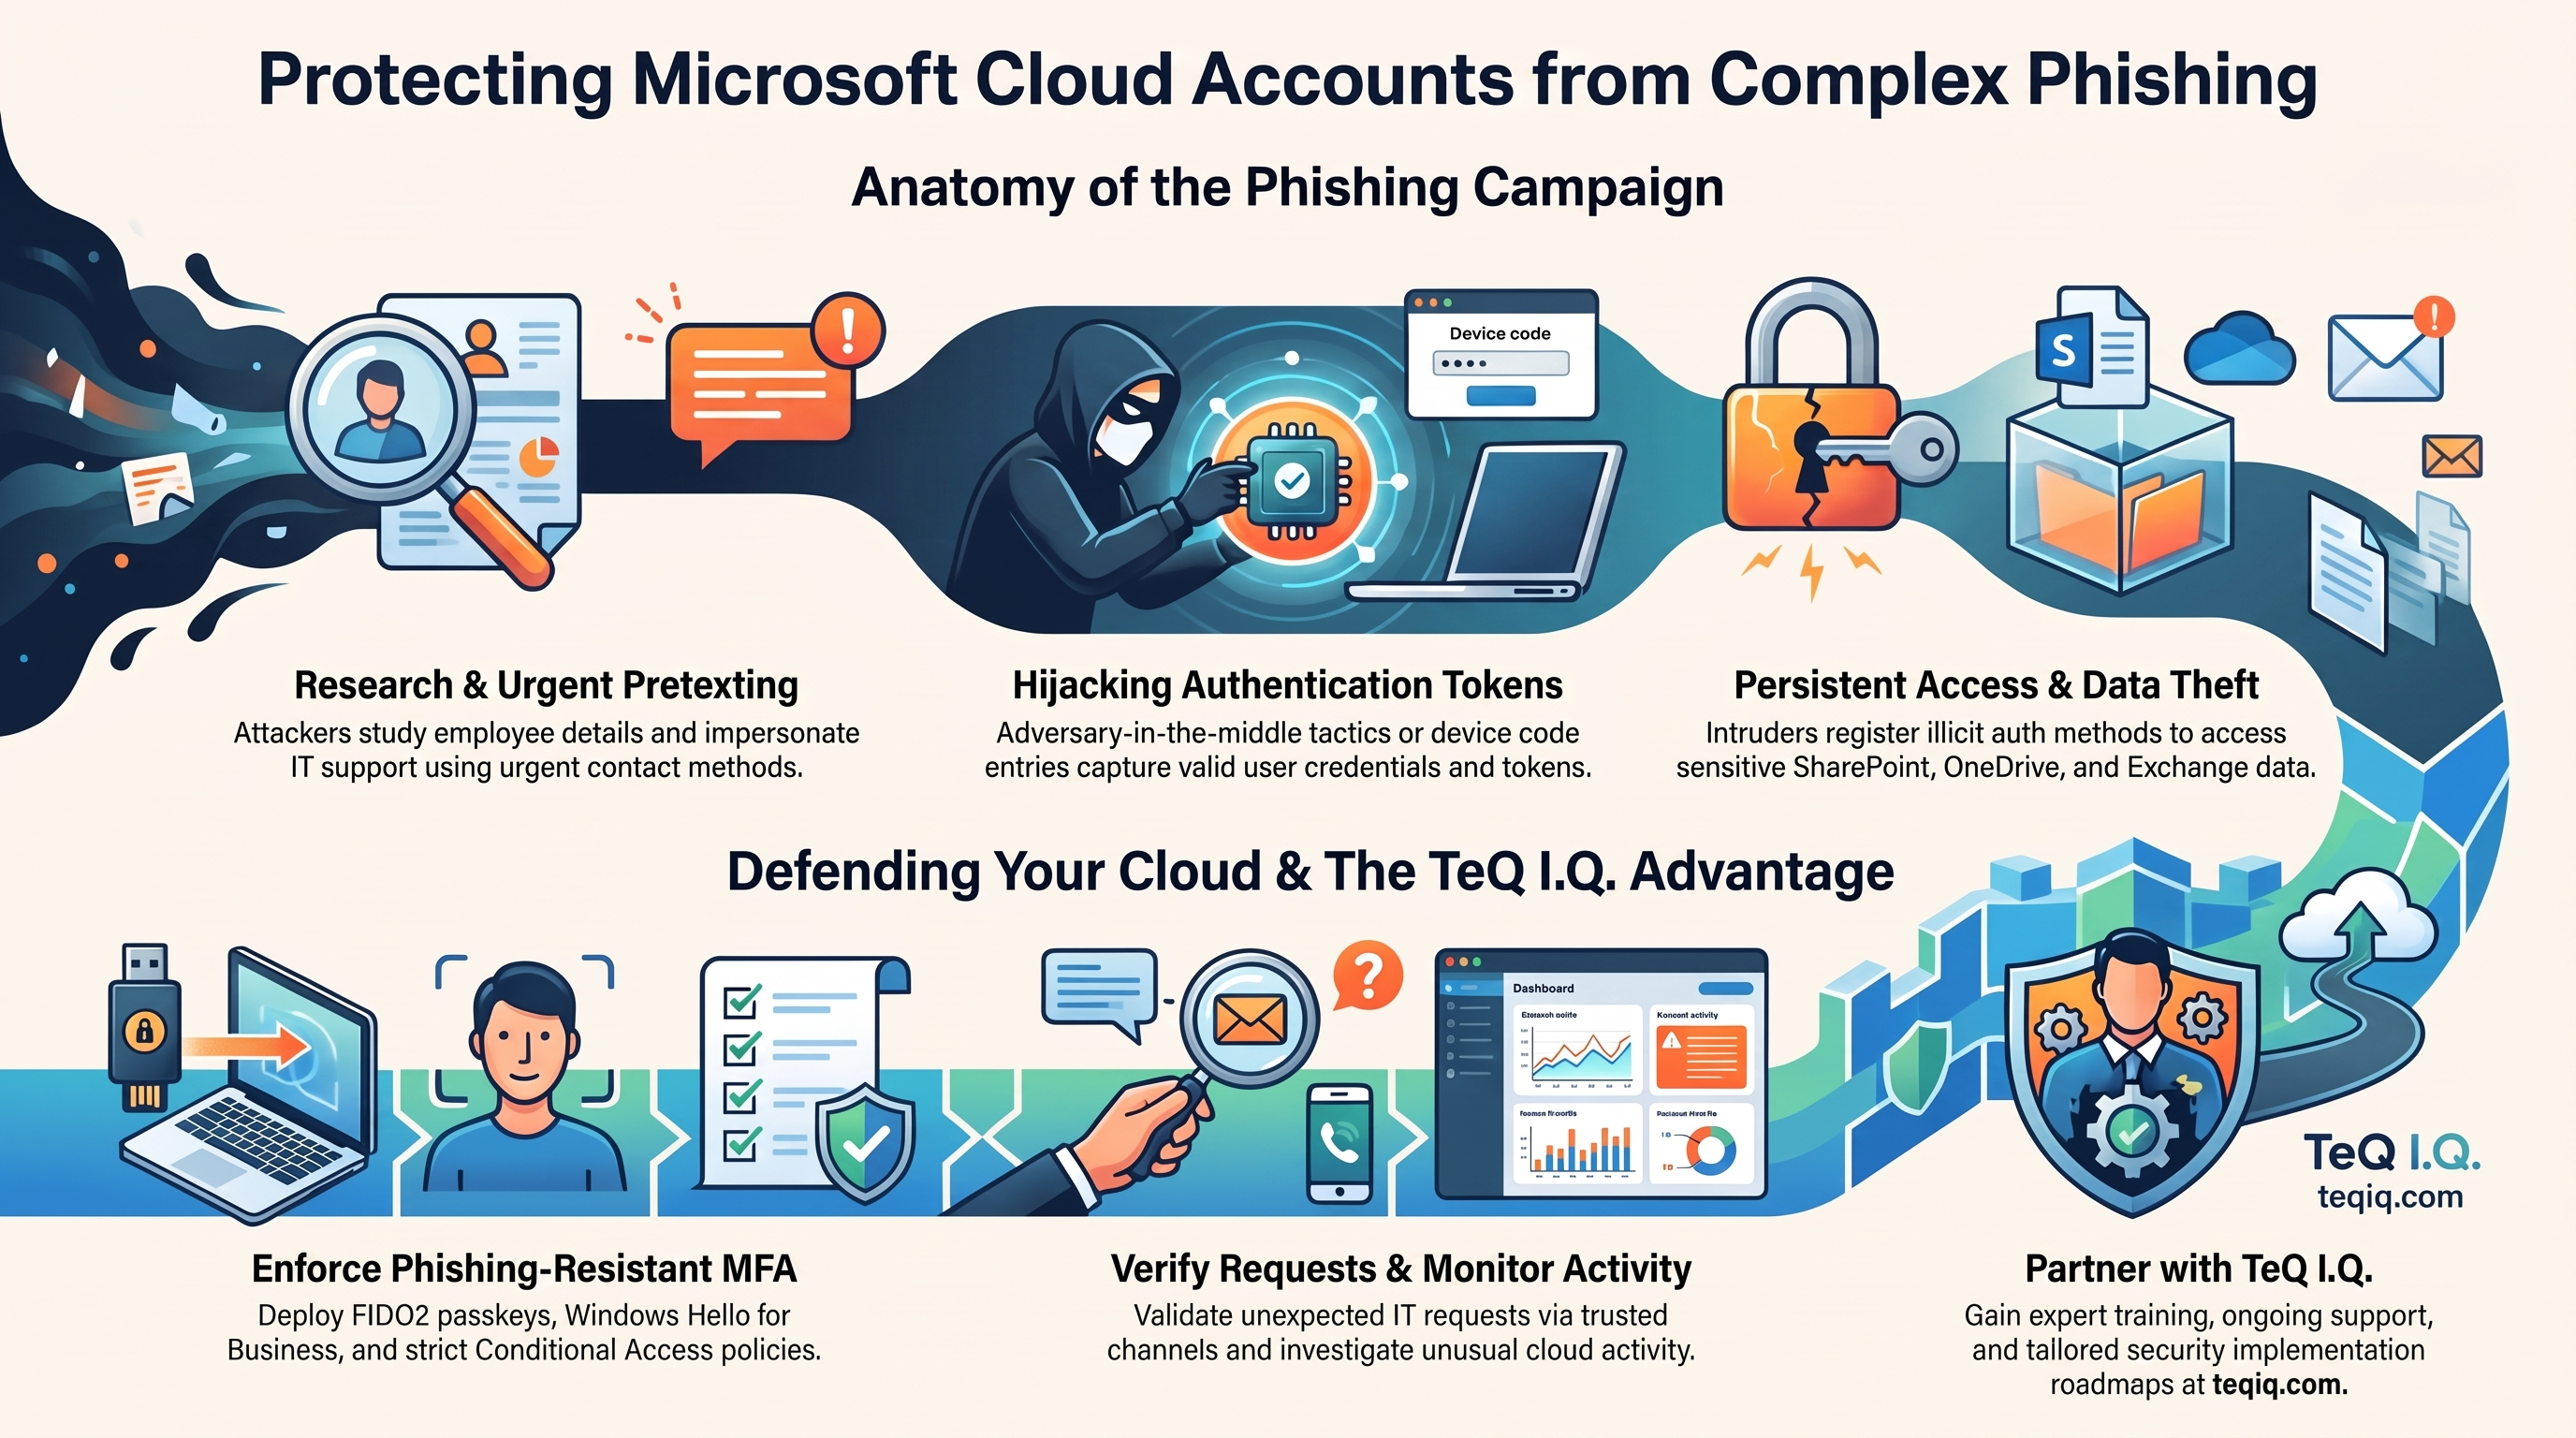
Research the Target
Attackers may study publicly available information about employees and company structures beforehand. These impersonation techniques can make an unexpected IT request seem more credible.
Create a Convincing Pretext
Next comes direct contact. The caller presents the authentication change as urgent, often while posing as IT support. Victims may then receive a text directing them to a website that resembles a legitimate Microsoft sign-in experience.
Hijack the Authentication Flow
The passkey itself is not necessarily the target. One approach uses adversary-in-the-middle phishing to capture credentials and session tokens. Alternatively, a victim may enter a supplied device code on Microsoft's legitimate authentication page and unknowingly authorize an attacker-controlled client.
Establish Persistent Access
Successful entry can enable further activity. An intruder may register another authentication method under their control. Microsoft has also observed reconnaissance through Microsoft Graph before attackers access SharePoint, OneDrive, or Exchange content available to the compromised user.
This progression can turn credential theft into a much broader threat to Microsoft cloud accounts.
Put Stronger Barriers Around Your Cloud
Businesses can reduce their exposure through a combination of technical safeguards and employee awareness. Microsoft recommends the following strategies:
- Use phishing-resistant MFA: FIDO2 passkeys or Windows Hello for Business can provide stronger protection through Conditional Access.
- Verify IT requests: Employees need a trusted channel to confirm unexpected authentication instructions before responding.
- Control unmanaged devices: Conditional Access policies can prevent untrusted hardware from reaching sensitive cloud resources.
- Review authentication changes: Treat unfamiliar devices or newly registered methods as potential warning signs, especially after unusual sign-ins.
- Watch cloud activity: Abnormal Microsoft Graph behavior, large file downloads, or suspicious mailbox access deserve closer investigation.
Attackers increasingly combine technical deception with convincing human interaction. Strong proactive measures around your company's Microsoft cloud accounts can make these elaborate schemes much harder to pull off.
Unless you have a highly capable in-house IT team, we recommend working with a provider that offers training, support, and an implementation roadmap like TeQ I.Q. has.
Ask How TeQ I.Q. can help You or Your Business. Go To Web Site https://www.teqiq.com/
TeQ I.Q. is for Customers who Embrace Change, Want Real Support With More Solutions to Increase Sales and Have More Time!
If this tip helps and you would like to donate click on the button. Thanks In Advance.
________________________________________________________________________________________________________
"Fortune Favors, Who Value Time over Money!"
"TeQ I.Q. was the 1st IT Company to Deliver Cloud Solutions since 2003"
Tech issues taking up your Time?
"TeQ I.Q. Makes Your Technology Secure and Protected"
Do you have Tech Frustrations like your Computer, Internet, Phone, Cellphone, Camera, TV, Car?
"We Take Away Your Tech Frustrations and Give You the Free Time You Deserve!"
Call Robert to ask all your Technology questions.
For Free Consultation Call Now Robert Black at (619) 255-4180 or visit our website https://www.teqiq.com/
Chase Bank and Others Trust TeQ I.Q. with their IT and TeQnology so can you!