"Share this Info and Help a Friend"
NEW: AI Mobile and Desk Phone Service!
"AI Reception, AI Summary, Call Recording Transcription"
Answer Calls and Text on your Desk Phone / Computer / Mobile Phone / Tablet.
TIME = LIFE "TeQ I.Q. Increases your TIME"
TeQ I.Q. is for Customers who Embrace Change, Want Real Support With More Solutions to Increase Sales and Have More Time!
Call Robert at 619-255-4180 to Easily set you up!
TeQ I.Q. Computer Repair, TeQ I.Q. TV, TeQ I.Q. Mobile, TeQ I.Q. Internet, TeQ I.Q. Phone
Fake Voicemails Are Phishing Scams:
YouTube Video "Fake Voicemails Are Phishing Scams"
Would your team be able to spot fake voicemails in their inboxes? Today's cybercriminals use transcript emails to direct people toward fraudulent login pages and capture account information. Learn more about it here.
Voicemail Alerts Make Convincing Bait
A voicemail alert rarely looks dangerous at first glance. Employees encounter these notices during an ordinary workday, so another automated message may not raise much suspicion. Unfortunately, threat actors are exploiting that familiarity on a massive scale.
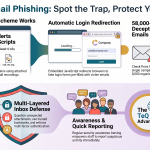
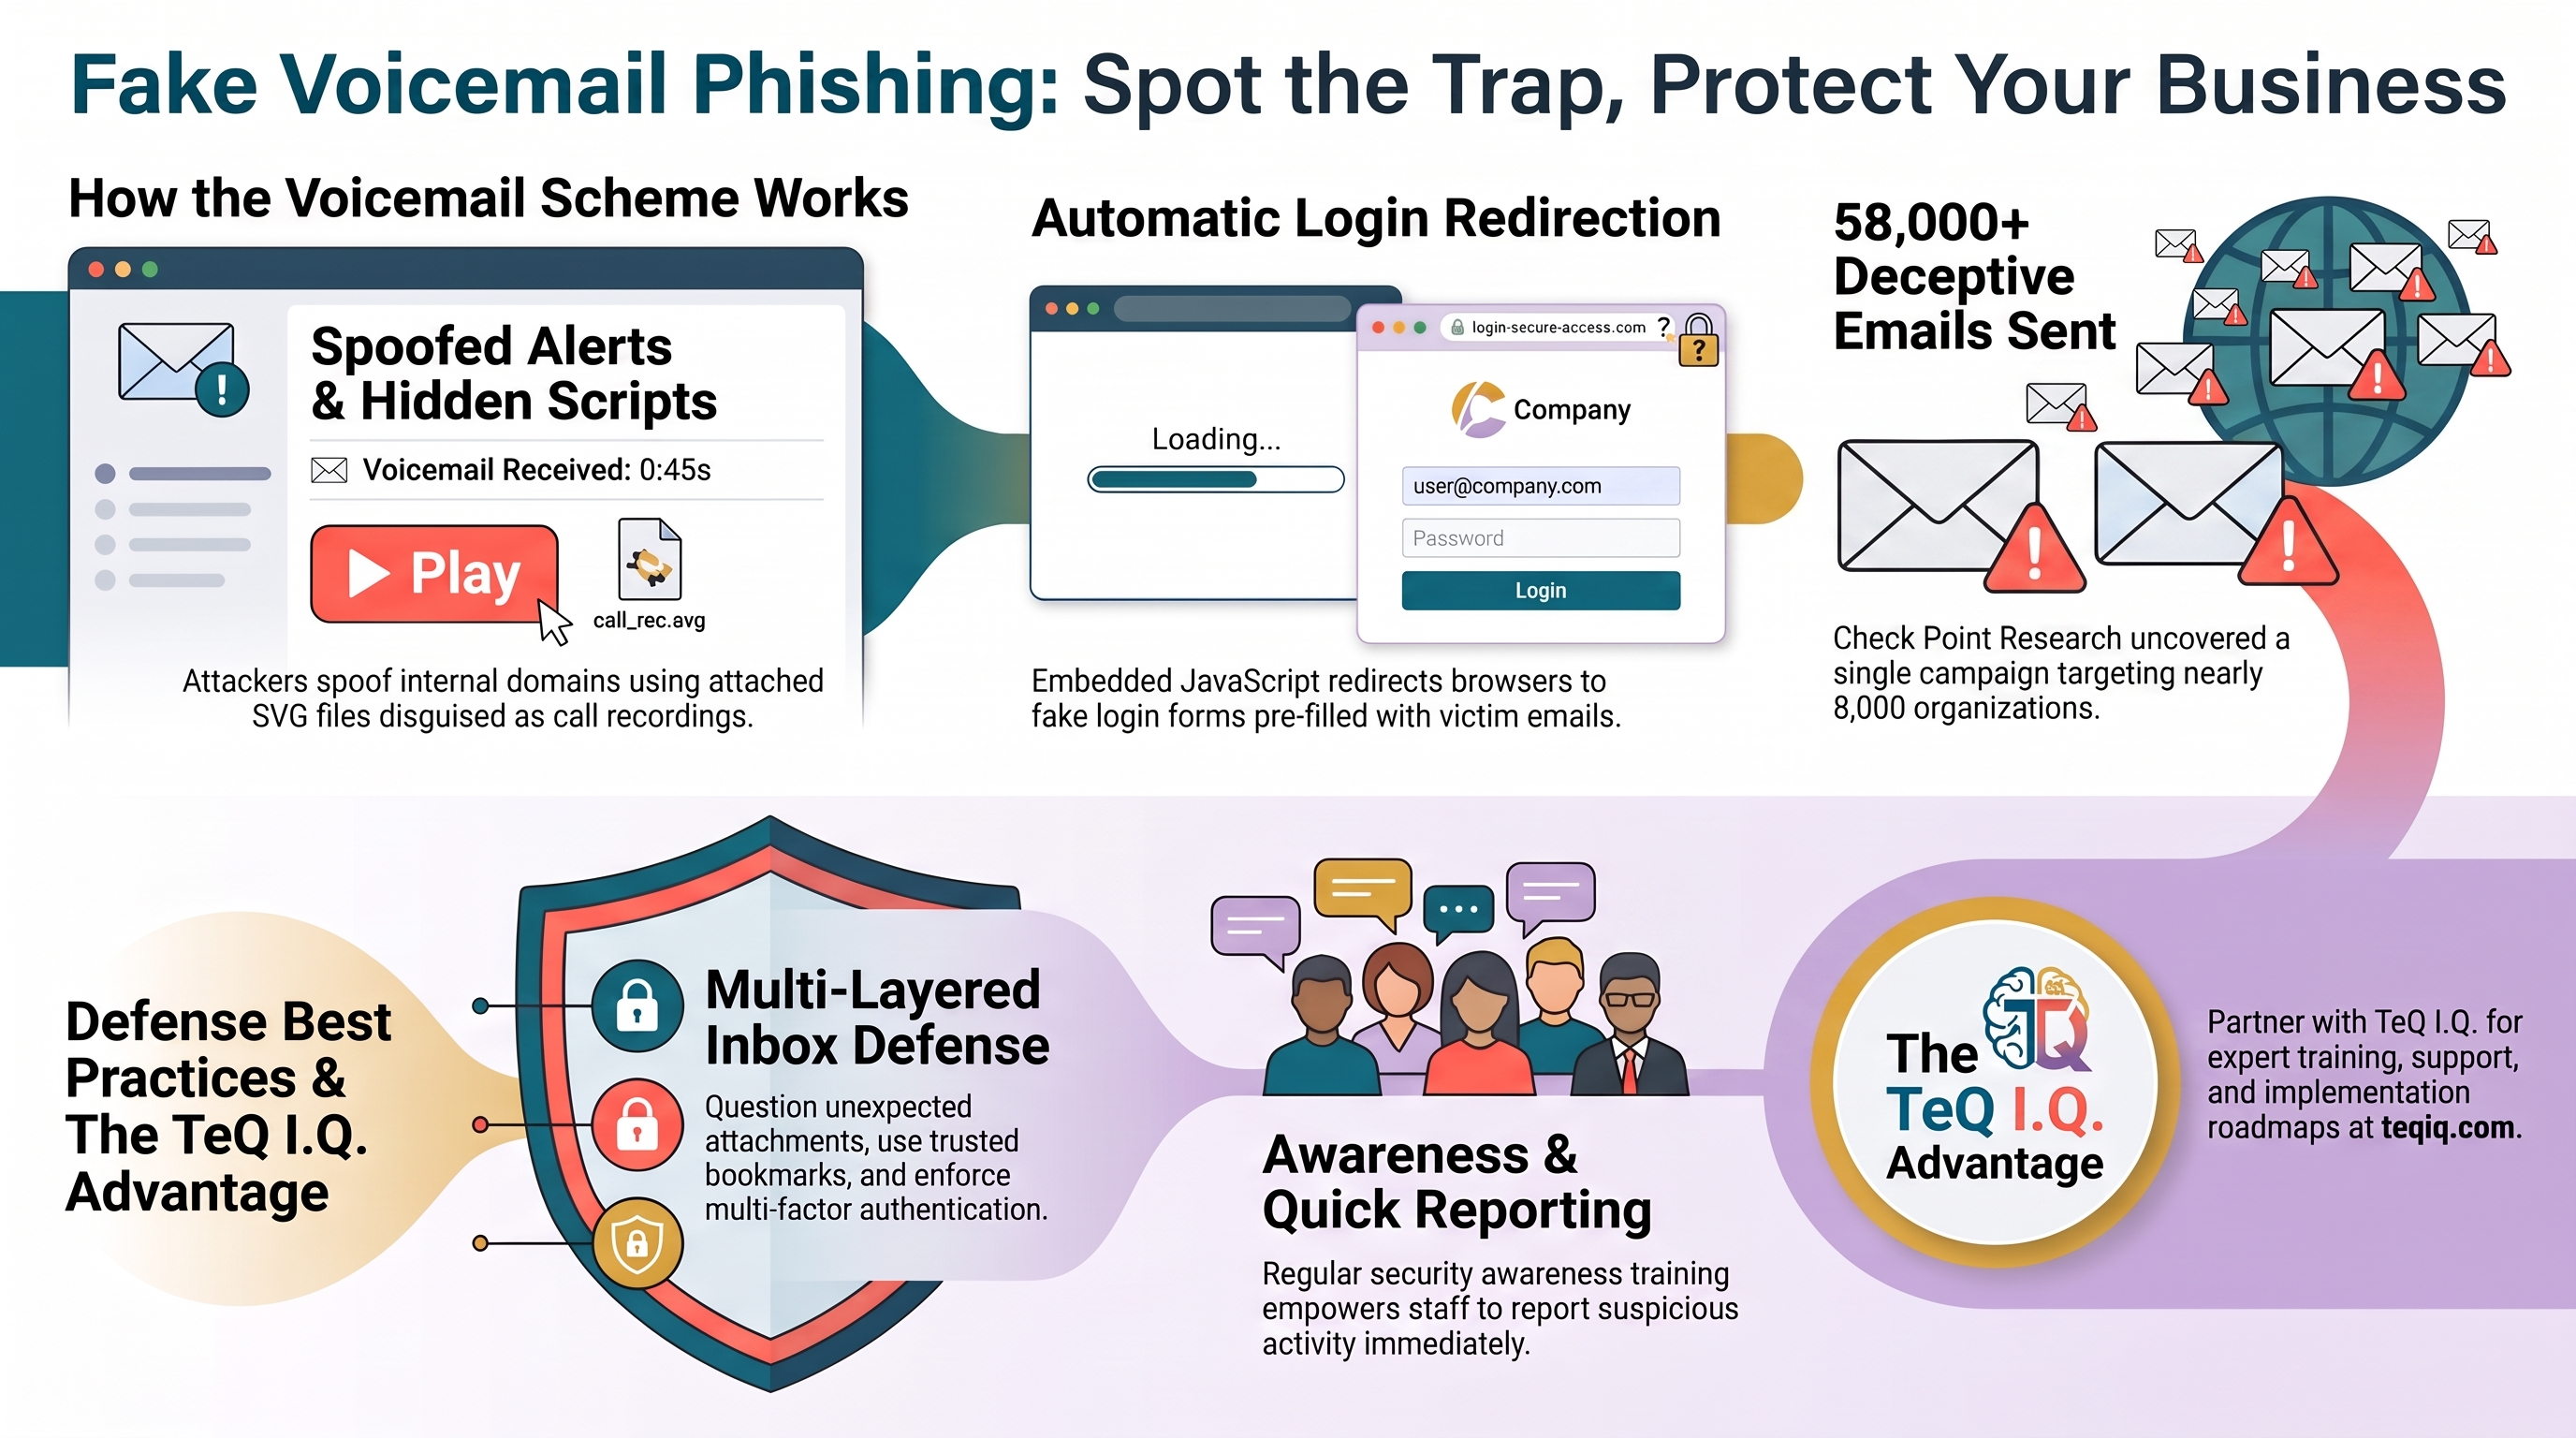
Check Point Research (CPR) uncovered a major phishing campaign that sent more than 58,000 deceptive emails to nearly 8,000 organizations between August 17 and 31. Tens of thousands of spoofed sender addresses helped the messages resemble legitimate transcript notifications.
How Does This Voicemail Scheme Work?
The campaign turns a routine notification into a credential phishing trap. Here's how the attack typically unfolds.
Mimic an Internal Alert
Attackers spoof the recipient's domain and use subject lines that resemble voicemail transcripts. The attached SVG file also looks like a call recording, which helps the message maintain its disguise.
Trigger the Redirect
SVG files can contain more than graphics. In this case, embedded JavaScript activates when the attachment opens and redirects the browser to a phishing page without exposing an obviously suspicious link.
Personalize the Login Trap
Because the URL contains the victim's email address, the site can automatically fill it into the login form, making the login page appear more convincing.
The goal of these fake voicemail transcripts is to steal credentials. Anyone who enters their account details hands that information directly to the criminals, potentially giving them access to the compromised account.
Another Version Goes After Google Accounts
The operation CPR uncovered isn't the only one using voicemail-themed phishing attacks. Security researcher Anurag documented a separate scheme that impersonates communication services and routes victims through several pages before displaying a fraudulent sign-in form.
This campaign specifically seeks Google credentials. A target follows malicious email links and eventually reaches a convincing imitation of an authentic login portal. Any information entered there goes to the criminals.
Fake voicemails make useful bait because missed calls naturally spark curiosity. Employees want to know who contacted them, which can encourage a quick response without careful verification.
Make Your Inbox Harder To Exploit
No security tool can catch every deceptive message. Create multiple layers of defense with the following workplace habits:
- Question unexpected attachments: Treat unusual file formats with extra caution, especially if you didn't expect them.
- Inspect the destination: Access accounts through trusted bookmarks or official websites instead of unsolicited messages.
- Strengthen authentication: Multi-factor authentication adds another barrier after password theft.
- Keep employees informed: Security awareness training should cover current workplace lures and explain how these schemes operate.
- Encourage quick reporting: Employees should alert IT staff when something seems suspicious.
Keep a Missed Call From Becoming a Bigger Problem
Criminals frequently disguise their schemes as familiar workplace communications. Fake voicemails show how an ordinary notification can become an effective security lure.
Teach your employees to verify unexpected attachments and login requests before they act. A brief check can stop a convincing message from turning into an account compromise.
Unless you have a highly capable in-house IT team, we recommend working with a provider that offers training, support, and an implementation roadmap like TeQ I.Q. has.
Ask How TeQ I.Q. can help You or Your Business. Go To Web Site https://www.teqiq.com/
TeQ I.Q. is for Customers who Embrace Change, Want Real Support With More Solutions to Increase Sales and Have More Time!
If this tip helps and you would like to donate click on the button. Thanks In Advance.
________________________________________________________________________________________________________
"Fortune Favors, Who Value Time over Money!"
"TeQ I.Q. was the 1st IT Company to Deliver Cloud Solutions since 2003"
Tech issues taking up your Time?
"TeQ I.Q. Makes Your Technology Secure and Protected"
Do you have Tech Frustrations like your Computer, Internet, Phone, Cellphone, Camera, TV, Car?
"We Take Away Your Tech Frustrations and Give You the Free Time You Deserve!"
Call Robert to ask all your Technology questions.
For Free Consultation Call Now Robert Black at (619) 255-4180 or visit our website https://www.teqiq.com/
Chase Bank and Others Trust TeQ I.Q. with their IT and TeQnology so can you!