"Share this Info and Help a Friend"
NEW: AI Mobile and Desk Phone Service!
"AI Reception, AI Summary, Call Recording Transcription"
Answer Calls and Text on your Desk Phone / Computer / Mobile Phone / Tablet.
TIME = LIFE "TeQ I.Q. Increases your TIME"
TeQ I.Q. is for Customers who Embrace Change, Want Real Support With More Solutions to Increase Sales and Have More Time!
Call Robert at 619-255-4180 to Easily set you up!
TeQ I.Q. Computer Repair, TeQ I.Q. TV, TeQ I.Q. Mobile, TeQ I.Q. Internet, TeQ I.Q. Phone
Exchange Bug Puts Email at Risk:
YouTube Video "Exchange Bug Puts Email at Risk"
What if cybercriminals could snoop through your organization's sensitive emails without hacking each account directly? A serious Microsoft Exchange bug gives attackers that opportunity through a mailbox-permissions flaw.
How Can Threat Actors Use This Microsoft Exchange Vulnerability?
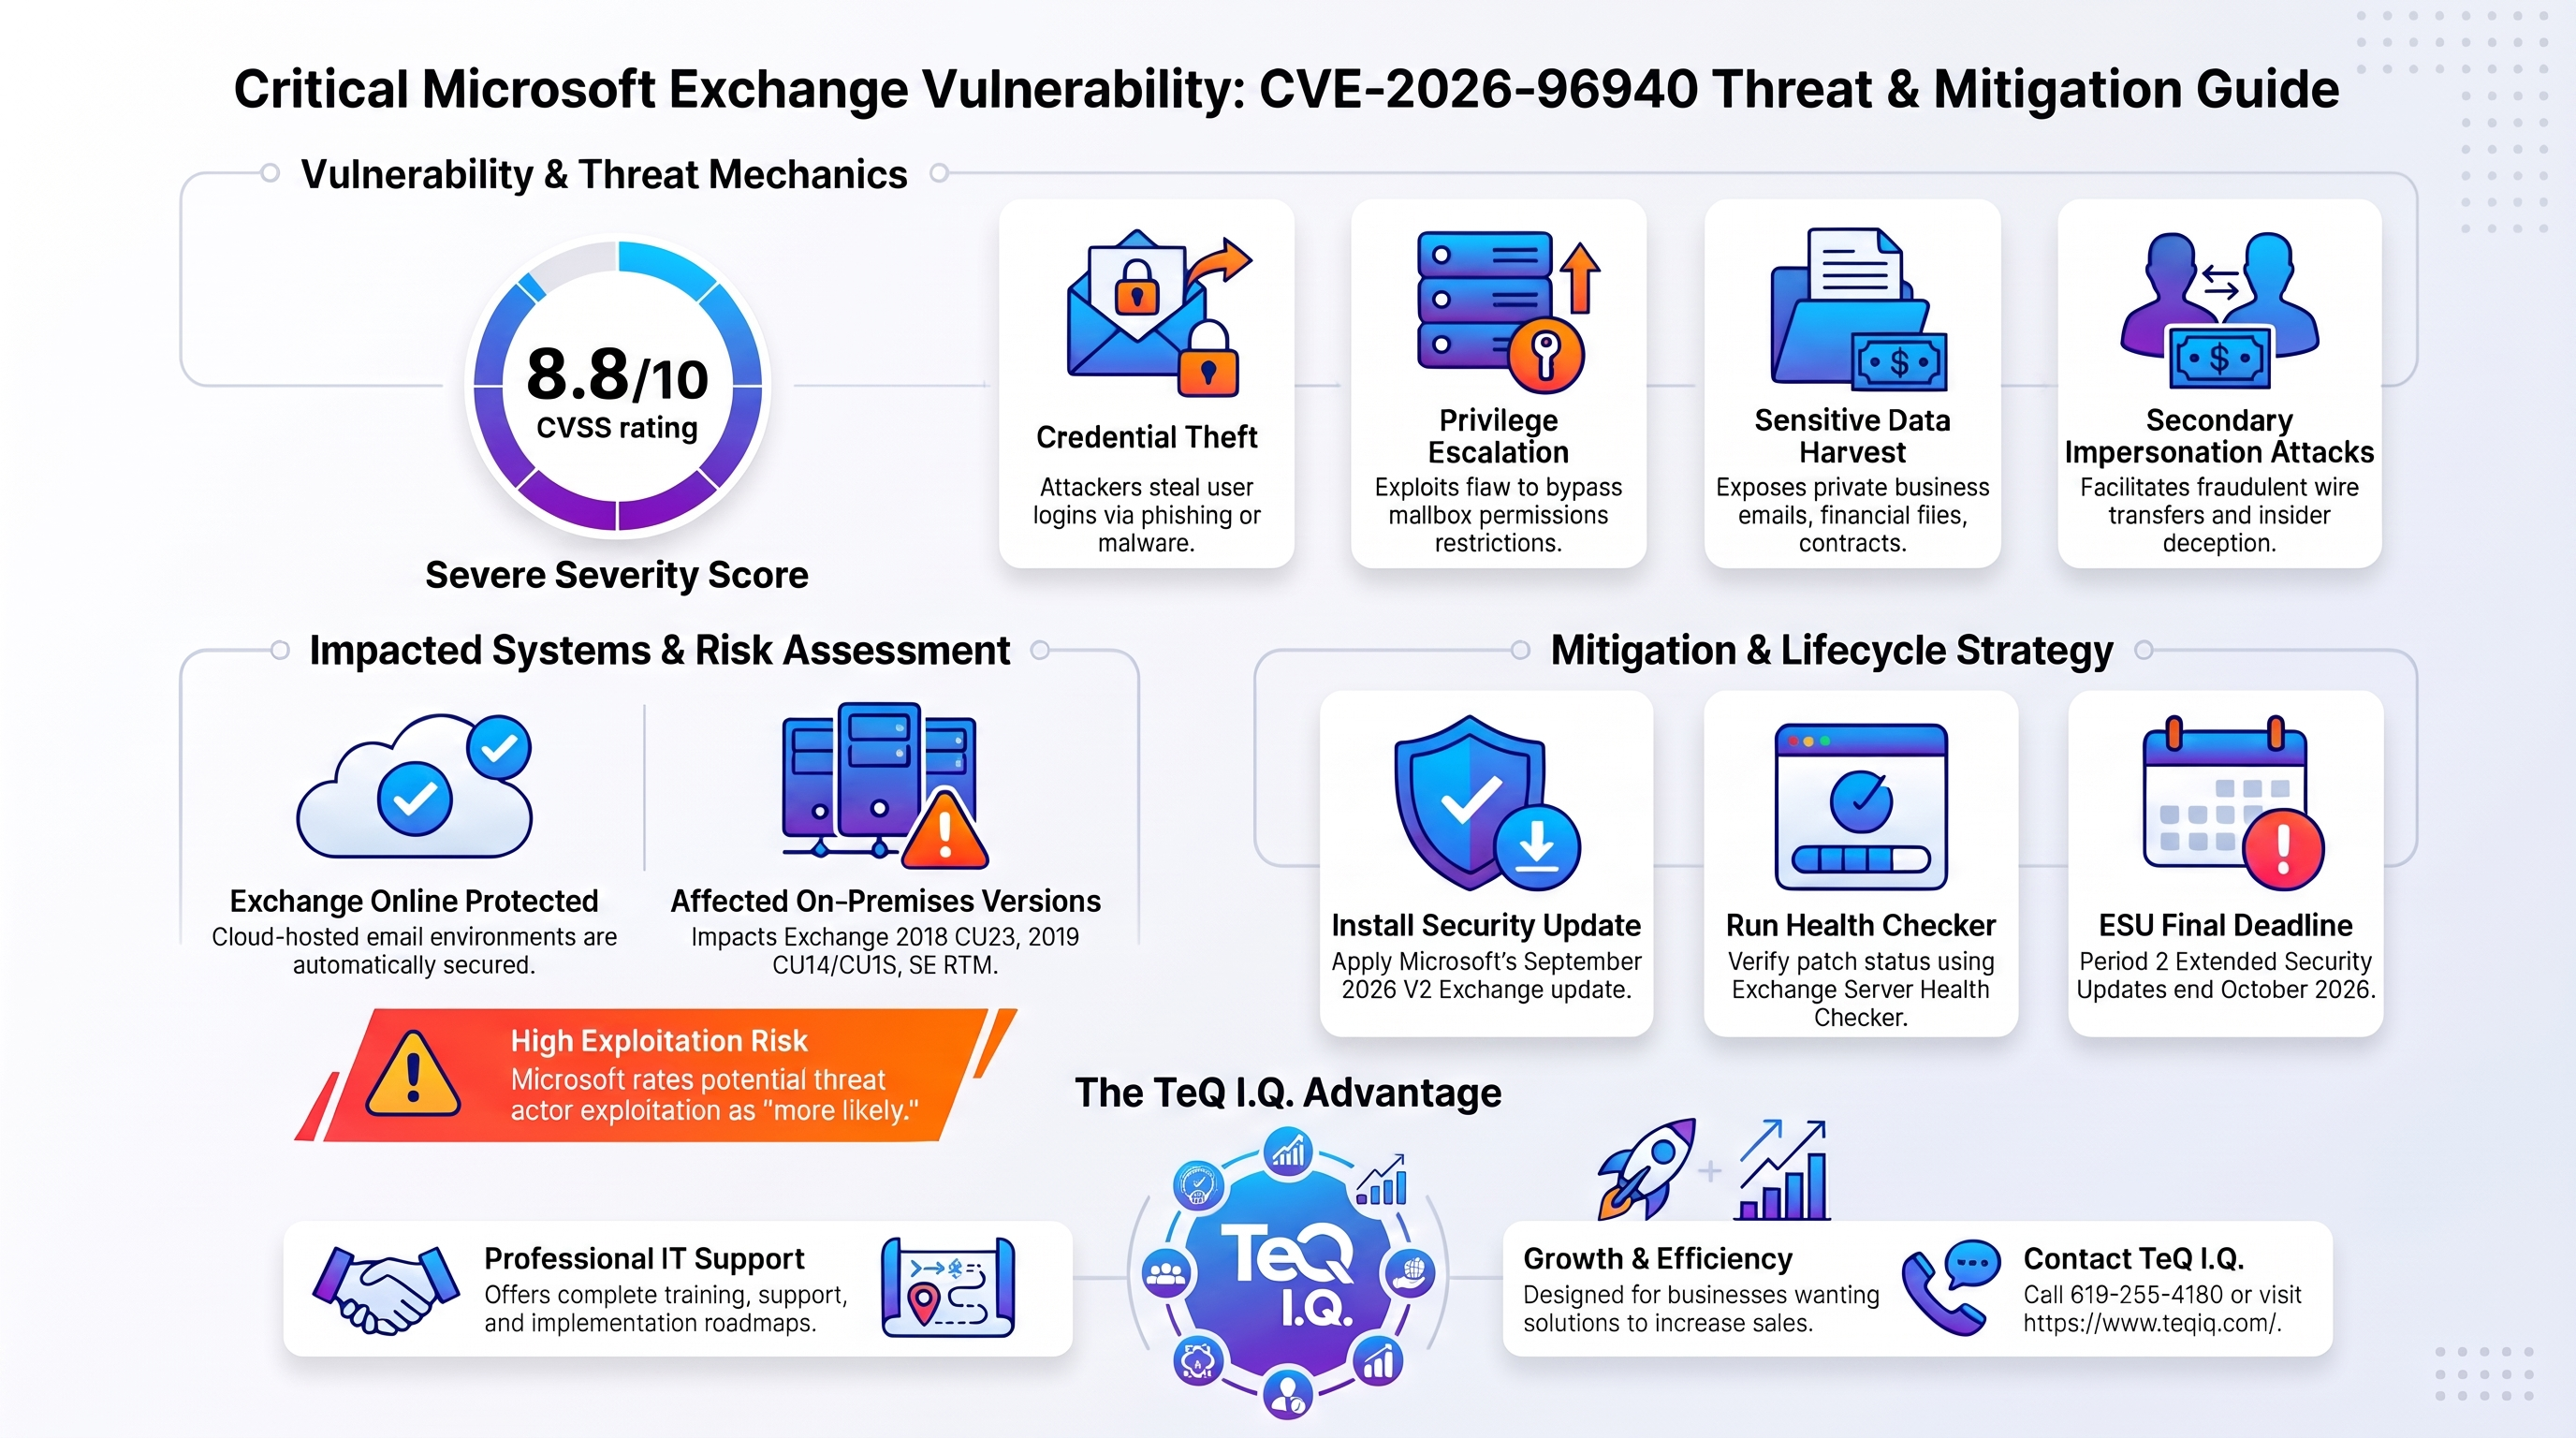
Tracked as CVE-2026-96940 with an 8.8/10 CVSS severity rating, this Microsoft Exchange bug is a privilege escalation vulnerability that allows attackers to access mailboxes beyond their authorized permissions.
The good news is that cybercriminals still need valid login credentials. Here's how they might exploit the flaw:
- Steal employee credentials: Attackers may use phishing emails, information-stealing malware, or dark-web-purchased passwords to access an ordinary employee's account.
- Escalate mailbox privileges: Once authenticated, attackers can exploit the vulnerability to bypass Exchange's normal access restrictions and gain unauthorized mailbox access.
- Harvest sensitive information: A compromised mailbox can expose private business discussions, financial records, and confidential contracts.
- Launch further attacks: Criminals can use the information to impersonate trusted individuals and trick employees into transferring money or disclosing more data.
A Swift Fix From Microsoft
Microsoft patched the issue on October 2 as part of its September 2026 V2 Exchange Server Security Updates. The original updates meant for this release were rolled out earlier on September 8. The main difference between the two versions is the fix for the cross-mailbox data access vulnerability.
After installing the update, the tech giant advises IT administrators to run Microsoft's Exchange Server Health Checker. This can help verify whether your system installed the patch successfully and recommend any other required actions.
Was Your Company Potentially Affected?
Exchange Online customers are already protected, but organizations must still update affected Exchange servers or Exchange Management Tools installations they maintain.
If you run affected Exchange Server installations, prioritize applying the update to prevent email data exposure and protect confidential business communications. Here are the versions impacted by the bug:
- Microsoft Exchange Server Subscription Edition RTM
- Microsoft Exchange Server 2016 Cumulative Update 23
- Microsoft Exchange Server 2019 Cumulative Update 15
- Microsoft Exchange Server 2019 Cumulative Update 14
According to Microsoft, there's no indication the flaw is being abused in the wild, and the US Cybersecurity and Infrastructure Security Agency (CISA) has not yet listed it in its Known Exploited Vulnerabilities (KEV) catalog.
It's still in your best interest to install the patch as soon as possible, however. Microsoft labeled this bug as "exploitation more likely," meaning threat actors may very well attempt to use it in their attacks.
Plan Ahead for Your Organization's Enterprise Email Security
Microsoft ended support for the 2016 and 2019 versions of Exchange Server last year, and only those who joined the Period 2 Extended Security Update (ESU) program can access the Microsoft Exchange bug fix.
This extension gives eligible customers access to the security updates released between May and October 2026. If your business has not yet enrolled in the program, consider migrating to Exchange Server Subscription Edition (SE) to receive the latest patches.
Period 2 also concludes in October 2026, after which Microsoft will no longer provide security patches or vulnerability testing for Exchange 2016 and 2019.
Unless you have a highly capable in-house IT team, we recommend working with a provider that offers training, support, and an implementation roadmap like TeQ I.Q. has.
Ask How TeQ I.Q. can help You or Your Business. Call 619-255-4180 or Go To Web Site https://www.teqiq.com/
TeQ I.Q. is for Customers who Embrace Change, Want Real Support With More Solutions to Increase Sales and Have More Time!
If this tip helps and you would like to donate click on the button. Thanks In Advance.
________________________________________________________________________________________________________
"Fortune Favors, Who Value Time over Money!"
"TeQ I.Q. was the 1st IT Company to Deliver Cloud Solutions since 2003"
Tech issues taking up your Time?
"TeQ I.Q. Makes Your Technology Secure and Protected"
Do you have Tech Frustrations like your Computer, Internet, Phone, Cellphone, Camera, TV, Car?
"We Take Away Your Tech Frustrations and Give You the Free Time You Deserve!"
Call Robert to ask all your Technology questions.
For Free Consultation Call Now Robert Black at (619) 255-4180 or visit our website https://www.teqiq.com/
Chase Bank and Others Trust TeQ I.Q. with their IT and TeQnology so can you!